What Is Crypto Mining Software
When I first heard about a plain explanation of crypto mining , I pictured folks tinkering with fancy rigs in their basements. But the reality is both simpler and messier. Crypto mining software is a program that borrows your computer’s brainpower to solve math puzzles for blockchain networks - that’s the proof-of-work model. The software races to add new blocks and pockets coins as a reward. If you want a crypto-for-dummies style take , think of it like a contest where the winner gets paid in crypto.
The phrase we keep circling back to is crypto mining software, and it shows up in many forms. Some of it is legit - a miner you choose to install. But plenty of it sneaks onto systems without permission. That hidden variety is what we call cryptojacking. A cryptocurrency mining machine might be a single PC or a whole rack of GPUs. Either way, it drains power and bogs things down.
Bitcoin alone uses about 137.9 terawatt-hours per year, more than some small nations.
Why Hidden Mining Is A Problem
Unauthorized crypto mining software isn’t just a minor nuisance. It can run a company hundreds to thousands of dollars per incident. I came across a case where one group pulled roughly $3 million by breaching Jenkins servers and mining Monero. That’s real money lifted straight from compute budgets.
And it’s not only about cash. When hardware runs hot around the clock, thermal stress sets in. In some regions, illicit crypto farms have triggered city-wide blackouts. On top of that, a compromised host often becomes a doorway for uglier attacks - ransomware or data theft.
What unauthorized mining does
- Drains your electric bill and cloud compute budget
- Slows down PCs and servers with high CPU use
- Creates heat and wear on hardware
- Opens a path for ransomware and lateral movement
Compromised hosts often become footholds for later ransomware, data theft, or lateral movement.
How Attackers Get In
Hackers have a whole playbook for dropping that crypto coin mining software onto your system. They prey on unpatched flaws in web apps or leave cloud APIs wide open. Sometimes they tuck the miner inside a fake download that mimics a legit tool.
One common path is through supply chain holes. A bad actor slips mining code into a build pipeline, and suddenly many machines run it. Another path is social engineering, where they poison search results so you click a look-alike site. The point is: they want your CPU, not your consent.
A Look At The ScreenConnect Trick
I came across a reported case where attackers spoofed utility sites like CrystalDiskInfo and HWMonitor. They packaged a ZIP with a real-looking exe and a malicious autorun.dll. When someone opened the utility, Windows loaded that dll, which silently installed ScreenConnect for remote control. That’s a sneaky way to plant persistent access.
After entry, the malware set up six persistence methods. It also tried to hide by hollowing into Microsoft-signed binaries and adding Defender exclusions for miners like lolMiner and gminer. Every five seconds it checked and repaired its own hooks. This is the kind of crypto mining software that really digs in.
Persistence mechanisms seen in that campaign
- Three scheduled tasks named Windows System Health and variants
- Two registry Run entries under WinSysCache__
- A Startup shortcut called RuntimeHost.lnk
- Auto-repair loop that recreates missing tasks every 5 seconds
Every 5 seconds the malware verifies persistence mechanisms and re-creates missing tasks, Run keys, or startup shortcuts.
DevOps Tools Turned To Mining
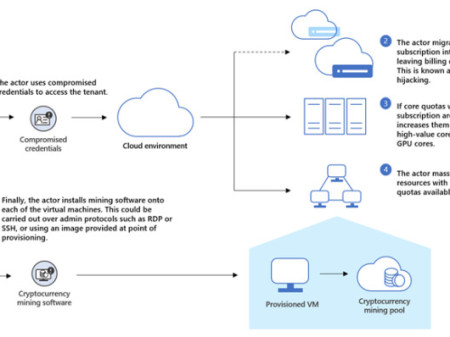
Another thread I pulled on was the abuse of DevOps tools. HashiCorp Nomad, Consul, Docker API, and Gitea frequently sit exposed thanks to loose configs. Attackers pounce on this. They submit a job that downloads XMRig and points it at a mining pool.
Telemetry shows a chunk of cloud environments host at least one of these tools, and some expose them to the public net. Among exposed setups, many are mis-configured. A single open Nomad could manage hundreds of client jobs, burning tens of thousands of dollars a month in resources.
Tools abused and why
- Nomad: default any-user-can-run-jobs policy left open
- Consul: script health checks can run arbitrary commands
- Docker API: exposed on 0.0.0.0:2375 gives root container control
- Gitea: old versions vulnerable to remote code execution
The Rocke Group Linux Case
Back in 2018 and 2019, a group called Rocke (Iron) hit Linux hosts hard. They exploited Apache Struts, Oracle WebLogic, and ColdFusion bugs. Once in, they dropped a backdoor and a Monero miner. They even used libprocesshider to hide processes from ps.
What stuck with me: they uninstalled cloud security agents like Tencent and Alibaba after gaining sudo. They followed the official uninstall guides to appear legitimate. They also blocked rival miners with iptables. This shows crypto mining software can be a cat-and-mouse game.
Rocke malware capabilities
- Persistence via cronjobs with random entries
- Process hiding using open-source LD_PRELOAD lib
- IPtables rules to drop competitor miner IPs
- Removal of cloud security product agents
Removes cloud-provider security agents after gaining full sudo access, mimicking legitimate admin actions.
A Warehouse Full Of GPU Rigs
In 2021, a company stumbled on something wild in their warehouse: cardboard boxes housing custom GPU mining rigs siphoning power off the network. They were mining Monero on the company’s dime. The heat and draw could have sparked fire risk and real financial loss.
Darktrace’s tools flagged odd internal traffic and self-signed SSL. Their response blocked outbound to mining pools and enforced normal pattern of life. This case shows hidden crypto mining software isn’t always on your laptop; it can be a physical box in a back room.
Jenkins Supply Chain Incident
Sonatype documented a 2018 breach where attackers leveraged Jenkins to drop a coin-miner. That miner harvested Monero and netted about $3 million. It’s a clear example of how open-source repos can spread mining malware at scale.
The takeaway for me is clear: supply-chain hygiene matters. If you don’t scan dependencies and patch CI/CD tools, you might host crypto mining software without knowing. It’s not just a personal PC problem; it’s a build pipeline problem.
Ways To Detect Mining Software
The good news is there are solid tools to catch this. AWS GuardDuty uses machine learning to flag crypto activity on EC2 or Lambda. It looks at DNS queries to mining domains and weird process trees. Detection time dropped from days to minutes in many setups.
Microsoft Defender for Endpoint surfaces Trojan and HackTool alerts tied to coin miners. It can block sideloading and odd scheduled tasks. For Linux, Wazuh is a light open-source monitor that alerts on SSH fails, cron changes, and CPU over 90%.
On the network side, a NIDS like Suricata can catch Stratum traffic on ports 3333 or 4444. It also flags DNS for known bad domains. Layered detection is the way to go.
Detection platforms and signals
- AWS GuardDuty: CryptoCurrency finding types for EC2, Lambda, runtime
- Microsoft Defender: Trojan:MSIL/CoinMiner and anomalous tasks
- Wazuh: high CPU rule, SSH brute force, cron mod alerts
- Suricata IDS: unencrypted and TLS Stratum mining pool traffic
Network Level Signs
If you’ve got a perimeter sensor in place, you can spot mining without ever touching endpoints. Watch for repeated connections to known pool IPs like pool.supportxmr.com. Also keep an eye on TLS to blacklisted domains. Those are strong tells that crypto mining software is phoning home.
A NIDS can catch mining traffic at the perimeter.
Warning Signs On Your Computer
For those of us on the ground, the first clue is often a PC that crawls for no obvious reason. Fans roar, battery drains fast. You might spot unknown processes like RuntimeHost.exe or SimpleRunPE.exe. And don’t be fooled by those best cloud mining apps for android ads promising easy coins - some are just fronts for hidden miners.
Check your task scheduler and registry Run keys if you’re brave. Outbound connections to weird domains are a red flag. If you see a earn free crypto apps that you don’t remember installing, dig in.
Signs of unauthorized mining
- CPU usage stuck above 90 percent for long stretches
- New scheduled tasks with vague health names
- Unexpected registry Run entries or startup links
- Network traffic to known mining pool domains
Stop The Crypto Mining Software
Prevention beats cleanup every time. Tighten identity with least privilege and MFA. Keep cloud APIs private. Segment networks so boxes can’t chatter with mining pools. On endpoints, switch on Defender or Wazuh with aggressive rules.
User training is huge. Teach folks to spot SEO-poisoned search results and fake AI chatbot links. If you run CI/CD, scan dependencies and generate SBOMs. That cuts off supply-chain abuse.
Layers of control to use
- Identity and access: enforce least-privilege IAM, enable MFA
- Cloud config: disable public Nomad/Consul, bind Docker local
- Network segmentation: block ports 3333 and 4444 outbound
- Endpoint protection: EDR block mode, ASR rules, Linux file integrity
IOCs To Block
If you want to check a crypto address against known bad actors, here are a few from past campaigns. Domains like direct-download.gleeze.com and blog.sydwzl.cn show up. IPs like 193.42.11.108 were used for C2. Monero wallets from Rocke and the ScreenConnect case are public.
You can import these into your SIEM or EDR. The SHA256 hashes for autorun.dll and SimpleRunPE.exe are also out there. Having a list helps automate blocking before damage.
Sample indicators to watch
- Domain: direct-download.gleeze.com
- IP: 193.42.11.108 (ScreenConnect C2)
- Monero wallet: 468VEByGGFQSN2bJG99ovhe5SG9SLxLAA9e2s7tWFxvBM33FAEP4JbwYHEeXexq8djYpDEHg9Jq6eGF3rREnAAc4UkjLd3E
- Mutex: Global\D3F4E2A1_Svc_ used by SimpleRunPE
All these IOCs can be imported into SIEMs, EDR platforms, or threat-intelligence feeds for automated blocking.
Thinking About Crypto Safety
Look, I’m not anti-crypto. But a legitimate crypto investment isn’t someone hijacking your laptop cycles. If you’re new, a beginner’s guide to cryptography will help you grasp keys and hashes. And how the crypto wallet works is a question worth answering before you store coins.
Those earn free crypto apps might sound sweet, but many hide crypto mining software. Stay skeptical. Patch your stuff, watch your task manager, and keep your cloud closed. That’s how we keep our machines ours.
I’ll leave you with this: the battle against hidden miners is ongoing. The more we share plain info, the harder it is for thieves to win. Keep your eyes open.
Comments on “How to Find and Stop Unauthorized Crypto Mining Software Hiding on Your System”
No comments yet. Be the first to share your thoughts.